Kernel-level anti-cheat is anti-cheat software that installs a driver into the Windows kernel, the privileged core of the operating system known as ring 0, so it can inspect memory, drivers and processes that an ordinary ring 3 program is not allowed to touch. BattlEye, Riot Vanguard, Easy Anti-Cheat, Tencent's Anti-Cheat Expert and EA's Javelin system all work this way on Windows. Since October 2024, Steam has required developers to declare it: any game that installs a client-side kernel-mode anti-cheat must name it on its store page, and those labels now cover games from Rust and DayZ to Battlefield 6.
The trade is easy to state. A kernel driver sees far more of the PC than a game can, which is why studios use one against cheats that hide below the game. That same reach is why a buggy or abused driver can crash Windows or help an attacker, and why players argue about privacy. Both sides have receipts. Ring 0 itself comes first, then how each major system loads, which games ship one, the safety record, Linux, and the link between kernel access and hardware bans.
What Kernel-Level Anti-Cheat Means
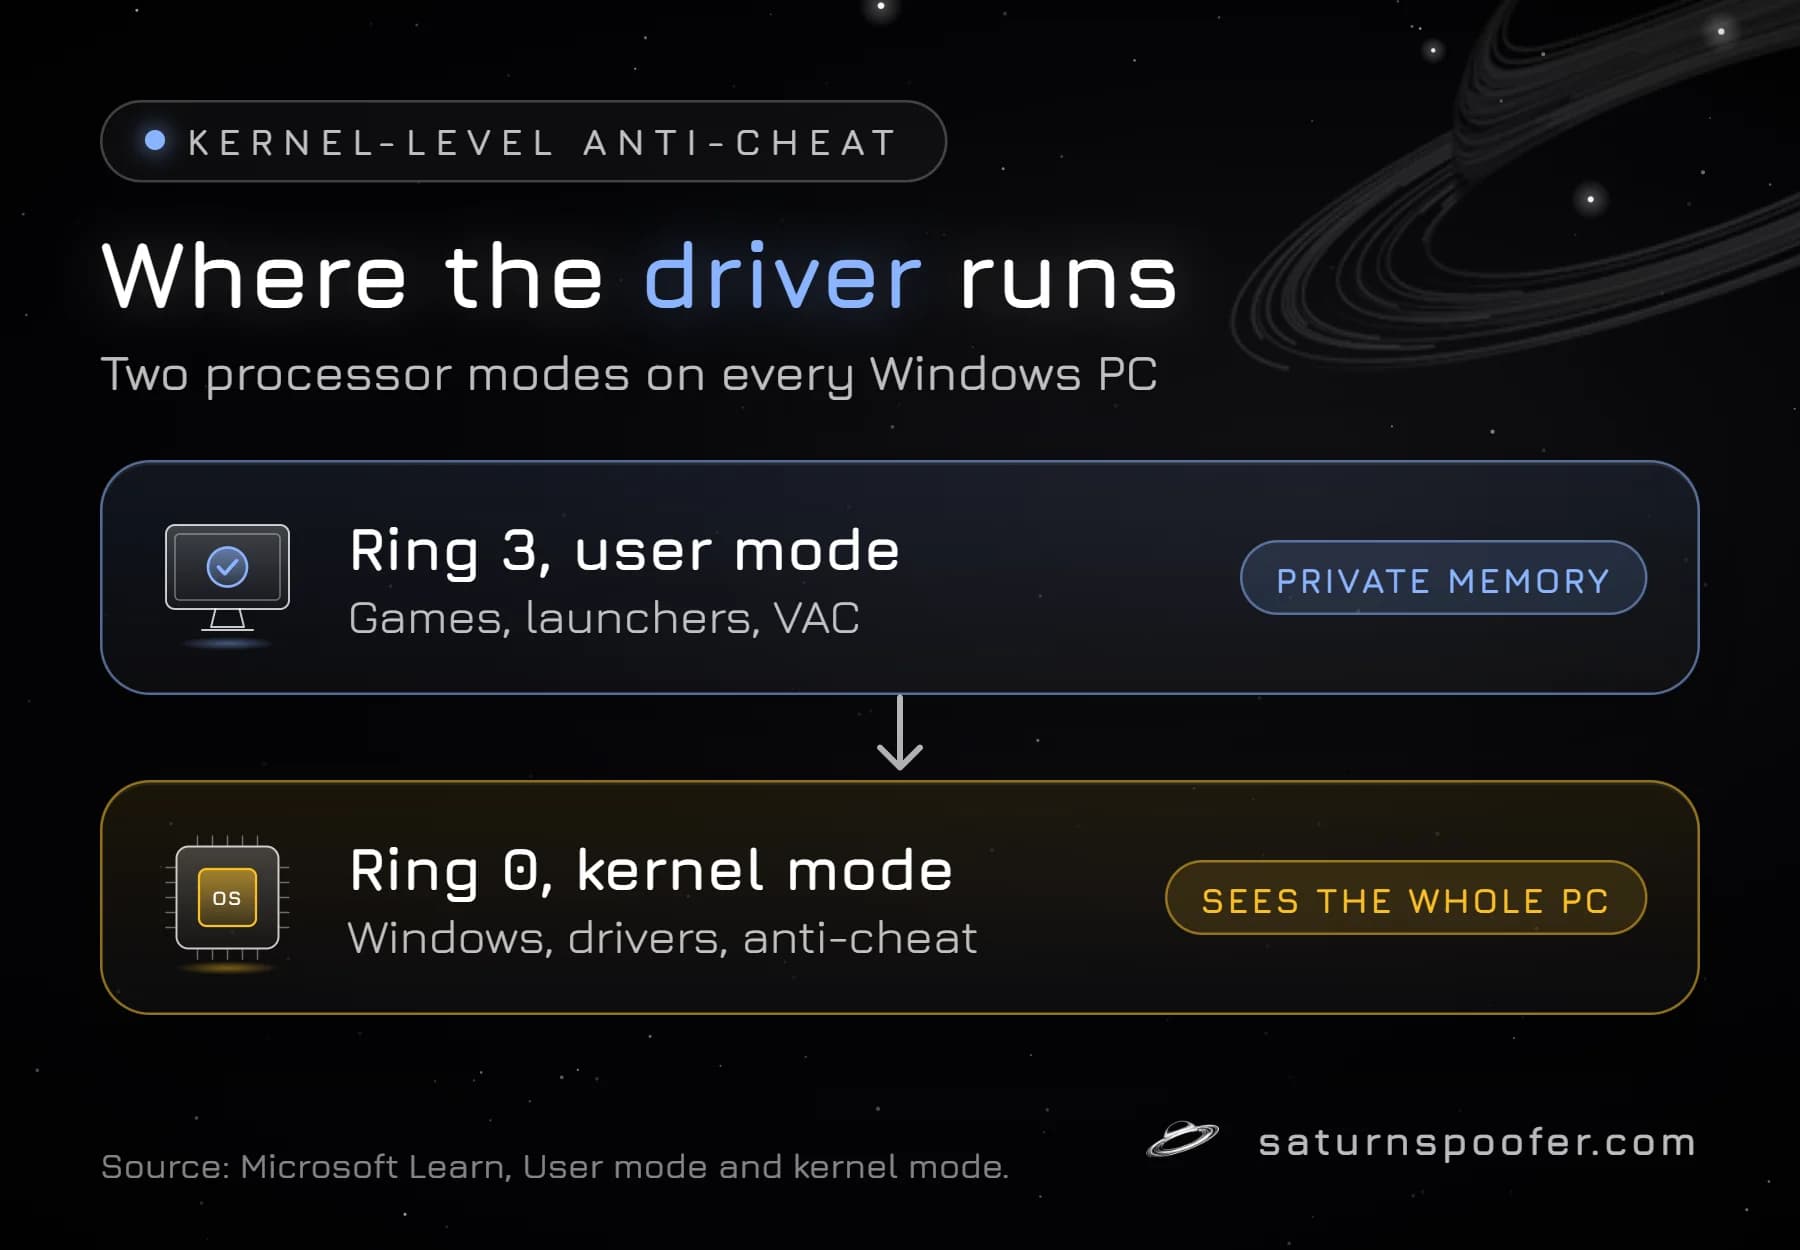
Kernel-level anti-cheat runs part of its code in kernel mode, the processor mode Windows keeps for its own core components and for drivers. Microsoft's user mode and kernel mode documentation splits a Windows PC into those two modes. Applications run in user mode, each one inside a private virtual address space, so one program cannot read or rewrite another program's data. Everything in kernel mode shares a single virtual address space with Windows itself. Microsoft states the cost in the same document: when a kernel-mode driver crashes, the whole operating system crashes with it.
The ring names come from the protection rings of x86 processors. Ring 3 is where games, browsers and launchers run. Ring 0 is where the Windows kernel and its drivers run. A user-mode anti-cheat, such as Valve Anti-Cheat on Counter-Strike 2, works from ring 3 under the same limits as the game it protects. A kernel anti-cheat adds a ring 0 driver to that setup, which gives it a view across the whole machine for as long as the driver is loaded.
Every kernel-mode driver has to clear Windows' signing rules before it can load. Microsoft's driver signing policy says that starting with Windows 10, version 1607, Windows will not load any new kernel-mode driver unless it has been signed through the Windows Hardware Dev Center portal. Anti-cheat makers ship signed drivers, and several of them refuse to start on a system whose kernel or signing checks have been tampered with. BattlEye's support FAQ lists a "Windows Kernel modification detected" error and says BattlEye cannot support systems that run a hacked Windows kernel.
Why Games Put Anti-Cheat in the Kernel
Game studios moved anti-cheat into the kernel because cheat makers got there first. Riot's 2020 /dev/null post on its anti-cheat kernel driver laid out the problem: cheat developers had begun exploiting vulnerabilities, or corrupting Windows' signature checks, to run cheat code at the kernel level. Code in kernel mode can hook the system calls that a user-mode anti-cheat depends on and hand back results that look legitimate. That breaks the user-mode model. A ring 3 scanner asking Windows "is anything touching the game?" gets whatever answer the ring 0 cheat chooses to give. The same Riot post noted that EasyAntiCheat, BattlEye and Xigncode3 were already using kernel drivers to protect big PC games.
EA makes the same case for its own system. Its security team's explainer on EA anticheat says PC cheat developers have increasingly moved into the kernel, that a cheat operating in kernel space can be functionally invisible to anti-cheat living in user mode, and that the only reliable way to detect and block those cheats is to operate in the kernel as well. Easy Anti-Cheat's player FAQ compresses the argument into one line: sophisticated cheats manipulate drivers, memory and hardware in ways normal applications cannot detect.
The contest did not stop at ring 0. Once kernel drivers became good at spotting cheat software on the gaming PC, some cheat makers switched to DMA cards, add-in PCIe hardware that reads game memory without running any code the anti-cheat can scan, often feeding a second computer. Kernel anti-cheats answered with platform checks on top of the driver. Battlefield 6's Steam listing, for example, says its Boot Protection requires both Secure Boot and TPM 2.0.
How a Kernel Anti-Cheat Works on Your PC
A kernel anti-cheat on Windows is usually three parts working together. The makers describe the outline in their support pages, and independent reverse-engineering write-ups fill in the parts the makers keep vague:
- A kernel driver loads into ring 0 and watches which processes try to open the game, which drivers and modules load, and whether the game's memory has been altered.
- A user-mode service talks to the driver and to the anti-cheat's servers. Easy Anti-Cheat's support pages describe this Windows service, which games install and remove along with themselves.
- A module inside the game process checks it from the inside and reports back to the service.
The clearest difference between the major systems is when the driver runs. Riot Vanguard is built to load as Windows boots, while Easy Anti-Cheat and EA's anticheat load with a protected game and leave when it closes:
| Anti-cheat | When it runs | Stated by |
|---|---|---|
| Riot Vanguard | From Windows boot (on-demand on PCs that pass Pre-Check) | Riot support |
| Easy Anti-Cheat | Only while a protected game is open | EAC support FAQ |
| EA Javelin Anticheat | Only while a protected game is running | EA security blog |
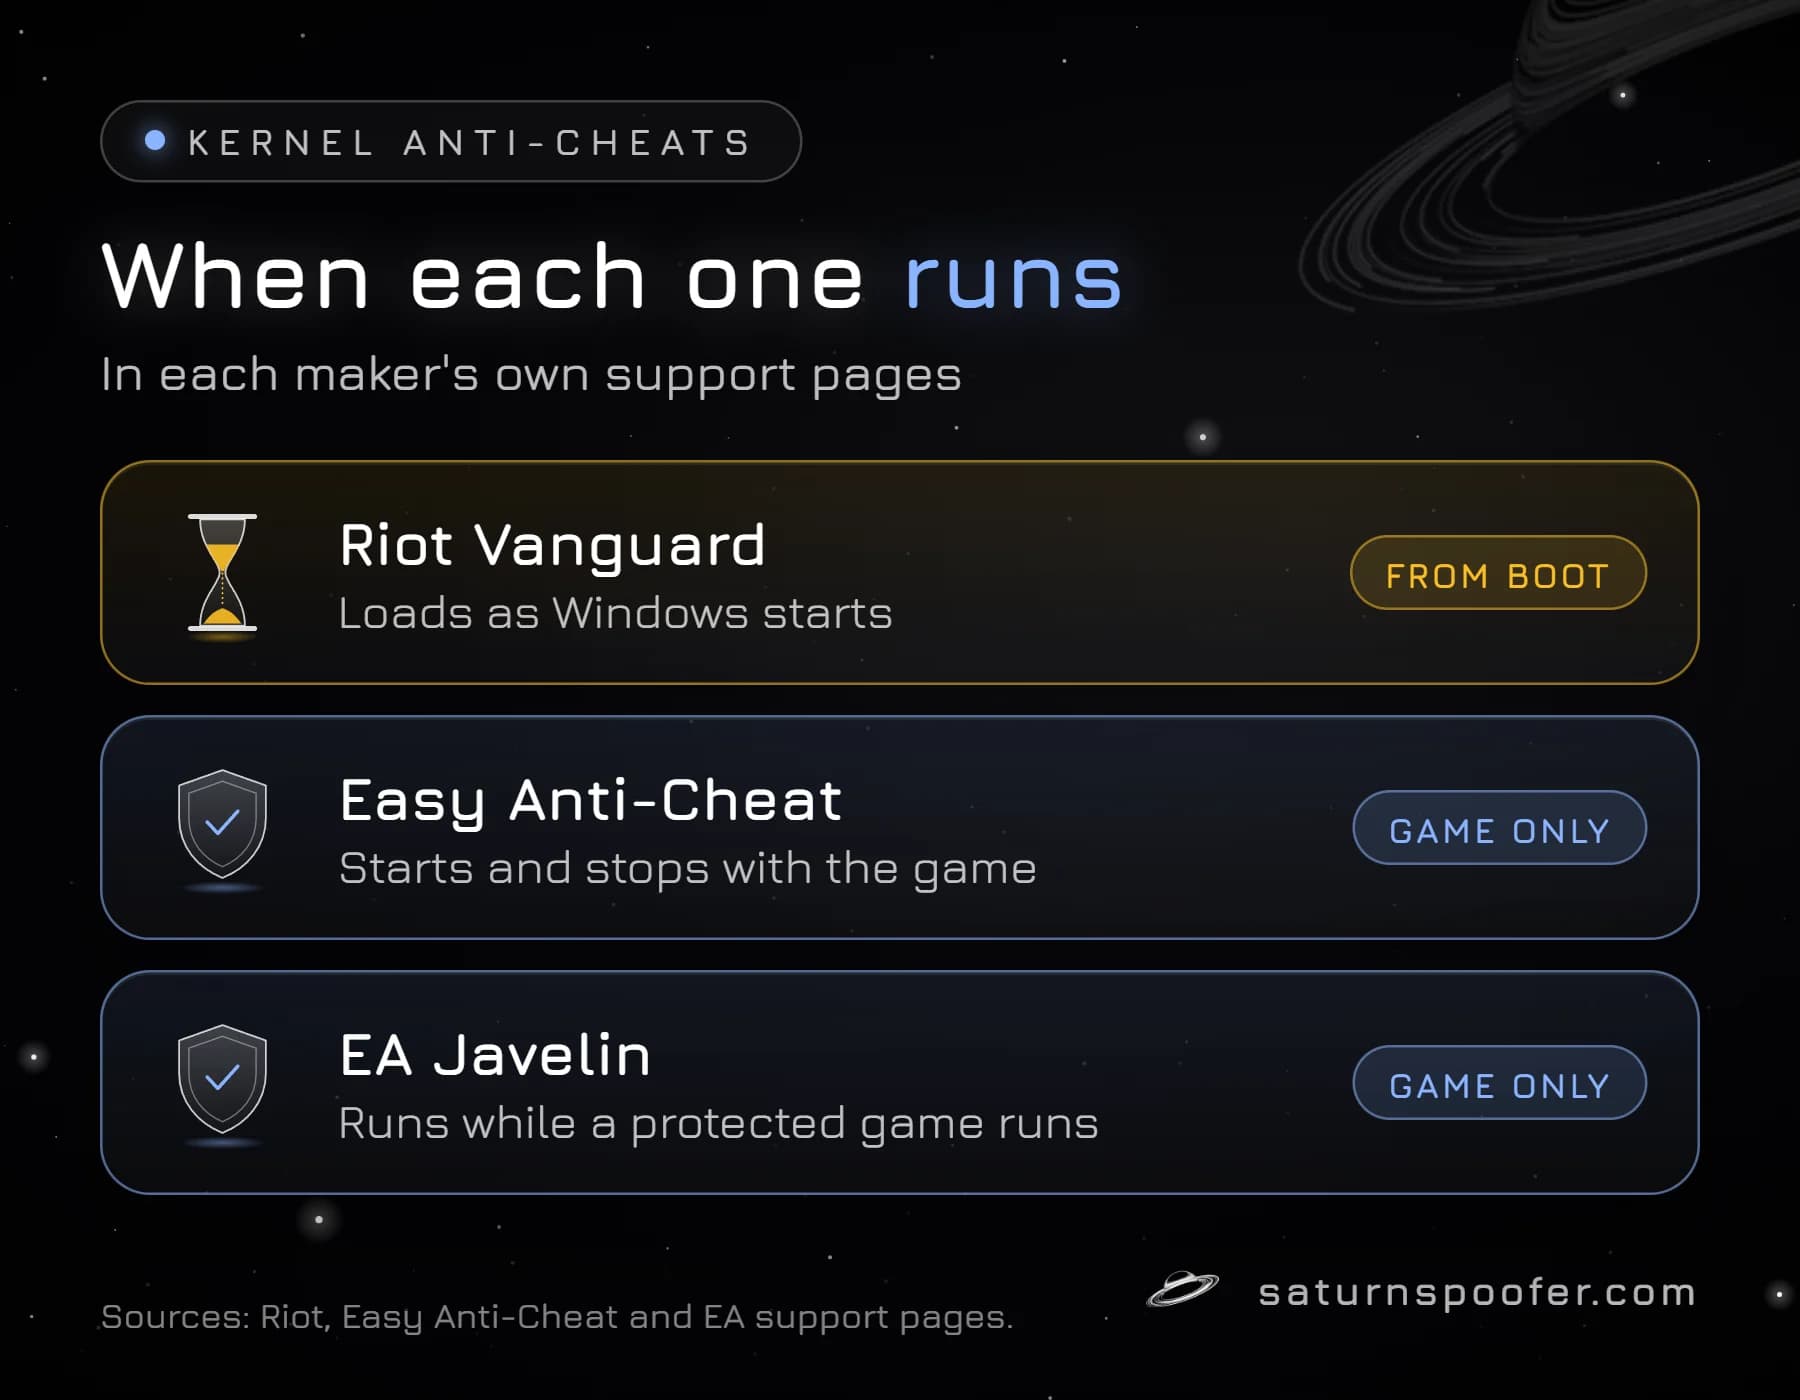
Boot loading gives a driver a head start: a driver in place before most others can inspect each one as it arrives, which reverse engineers cite as the reason Vanguard insists on loading first. It is also why Riot says that if you disable Vanguard and later want to play Valorant, you need to restart the PC. Game-launch loading keeps the driver off the system while you are not playing. EA puts it plainly: EA anticheat only runs when a game with EA anticheat protection included is running. Independent analyses describe BattlEye the same way, loading its driver with the game and unloading it on exit.
Which Anti-Cheats Run in the Kernel
Five kernel anti-cheats cover most competitive PC games on Windows, and each maker describes its kernel component in its own words. So the short answer to "is BattlEye kernel-level?" is yes, and the same is true of the other four systems below.
Riot Vanguard
Riot Vanguard protects Valorant and League of Legends, and Riot Games wrote it in-house. Riot's support page says Vanguard combines a kernel mode driver with a client that stays active while a Riot game is running, and Riot's own wording is that Vanguard is "usually an on-boot application". PCs that meet Riot's Pre-Check requirements can start and stop it on demand without a full restart. That boot-time driver is the context for what Riot Vanguard looks for in ranked Valorant and League matches.
Easy Anti-Cheat
Epic Games owns Easy Anti-Cheat and offers it through Epic Online Services. The support FAQ for what Easy Anti-Cheat does says it needs kernel-level access on Windows, yet stays off while Windows boots and never idles in the background: it starts when a protected game launches and stops when that game closes. Its site claims more than 200 protected games and more than 35 million players a month. Steam labels Easy Anti-Cheat as kernel-level on Rust and Dead by Daylight, and Fortnite, Epic's own game, runs it as well. Apex Legends was an EAC game for years, but EA switched its PC version to EA Javelin Anticheat on September 29, 2026, so the Easy Anti-Cheat label still on its Steam page is out of date.
BattlEye
What BattlEye does at the kernel level is spelled out on its own homepage, which describes a "fully proactive kernel-based protection system" plus continuous scanning of the player's system. The company started in 2004 as a third-party tool for the Battlefield series, and its support FAQ names its Windows driver, BEDaisy.sys. Steam's kernel-level label lists BattlEye on DayZ and Escape from Tarkov.
Anti-Cheat Expert
Tencent's Anti-Cheat Expert (ACE) sells a PC game security stack that, in its own English copy, reaches "from Ruggedization to Drive Protection". Its Chinese site lists driver protection next to security hardening and cloud scanning for PC games. Steam marks ACE as a kernel-level anti-cheat on Arena Breakout: Infinite and Delta Force.
EA Javelin Anticheat
EA Javelin is the name Steam shows for Electronic Arts' in-house system on Battlefield 6, and that listing adds Boot Protection that needs both Secure Boot and TPM 2.0. EA's security blog calls EA anticheat "a kernel-mode anti-cheat and anti-tamper solution developed in-house", and says it uninstalls itself once you have removed every EA game that uses it. Apex Legends joined the Javelin list when EA moved the game over from Easy Anti-Cheat.
Denuvo, KSS and Other Kernel Systems
Steam's disclosure field also surfaces kernel anti-cheats that most lists skip. ARC Raiders names Denuvo as its kernel-level anti-cheat, after Embark moved the game off Easy Anti-Cheat during 2026. PUBG: Battlegrounds names KSS, Krafton Security Services. Counter-Strike 2 names Valve Anti-Cheat, which Steam does not mark as kernel-level, which makes VAC the easiest user-mode example to point to in competitive PC gaming.
Which Games Use Kernel-Level Anti-Cheat
Steam is the quickest place to check whether a game uses kernel-level anti-cheat. On October 30, 2024, Valve told developers that a game installing a client-side, kernel-mode anti-cheat must fill in a new anti-cheat field on its store page, while games with other kinds of anti-cheat may fill it in by choice. The field can also flag that an anti-cheat leaves files behind after the game is removed. Games sold outside Steam, such as Valorant, League of Legends and Fortnite, rely on their publishers' own statements. These are the labels we read for major games:
| Game | Kernel anti-cheat | Source |
|---|---|---|
| Valorant | Riot Vanguard | Riot |
| League of Legends | Riot Vanguard | Riot |
| Fortnite | Easy Anti-Cheat | Epic |
| Apex Legends | EA Javelin | EA |
| Rust | Easy Anti-Cheat | Steam |
| Dead by Daylight | Easy Anti-Cheat | Steam |
| DayZ | BattlEye | Steam |
| Escape from Tarkov | BattlEye | Steam |
| Battlefield 6 | EA Javelin | Steam |
| Arena Breakout: Infinite | Anti-Cheat Expert | Steam |
| Delta Force | Anti-Cheat Expert | Steam |
| ARC Raiders | Denuvo | Steam |
| PUBG: Battlegrounds | KSS | Steam |
| Counter-Strike 2 | None (VAC is user mode) | Steam |
Any list of games with kernel-level anti-cheat goes stale, because publishers switch systems. ARC Raiders, Apex Legends and PUBG all run a different system today than older lists claim, so the store label on the day you check is the answer to trust.
Is Kernel-Level Anti-Cheat Safe?
Kernel-level anti-cheat is only as safe as the driver it installs, and the record has evidence for both camps. The makers argue that the risk is contained. Easy Anti-Cheat's FAQ says running software in the kernel does not carry a significantly higher privacy or security risk than software running with admin privileges, and that third-party vendors audit its code. EA says it hired independent security and privacy firms to review EA anticheat, and that it hashes the information it collects into unique identifiers and throws the originals away.
Critics point to what happens when kernel code goes wrong:
- Abused drivers. In 2022, Trend Micro reported a ransomware actor using mhyprot2.sys, the signed anti-cheat driver from Genshin Impact, to kill antivirus processes. The victims did not need Genshin Impact installed; the attackers brought the driver along.
- System crashes. A failing kernel driver takes Windows down with it. The July 2024 CrowdStrike outage came from a security product, not an anti-cheat, yet Microsoft estimated it hit 8.5 million Windows devices, and critics use it as the example for any third-party code in ring 0.
- Privacy and trust. A ring 0 driver can see the whole machine while it runs, and players cannot audit closed-source code. Academic work presented at ARES 2024 argued that kernel anti-cheats share technical traits with rootkits, while acknowledging they serve a defensive purpose.
- Clashes with Windows security. BattlEye's FAQ says its driver was blocked on Windows 11 PCs with Kernel-mode Hardware-enforced Stack Protection turned on, and that BattlEye itself blocks some third-party drivers with known security holes that cheats can exploit.
The habits that follow from that record are dull but useful: install a kernel anti-cheat only through the official game or launcher, keep Windows updated, and remove games you have stopped playing so their drivers leave with them.
Kernel Anti-Cheat on Linux and Steam Deck
Kernel anti-cheat built for Windows does not carry over to Linux, because a Windows kernel driver has no Windows kernel to load into under Proton or Wine. Epic announced Easy Anti-Cheat support for Linux, Mac and Steam Deck on September 23, 2021, including games running through Wine and Proton, but each developer has to switch that support on in the Epic Online Services portal. Many studios with competitive modes leave it off. GamingOnLinux pointed out that Steam's kernel anti-cheat label helps Steam Deck and desktop Linux players spot games whose developers block Proton.
Kernel Access and Hardware Bans
Kernel access is what lets an anti-cheat read serial numbers straight from the hardware: disk serials, motherboard SMBIOS data, network adapter MAC addresses, TPM keys and more. Publishers use those values for bans tied to hardware serials, which keep a PC out of a game even after the player creates a new account. EA says EA anticheat turns what it collects into hashed identifiers, and Riot's support site says a Riot HWID ban, which can follow a cheating flag, bars that person from every Riot game and every account on Riot's platform. Whether a cheater gets an account ban, a hardware ban or both is the publisher's call; the kernel driver supplies the identifiers.
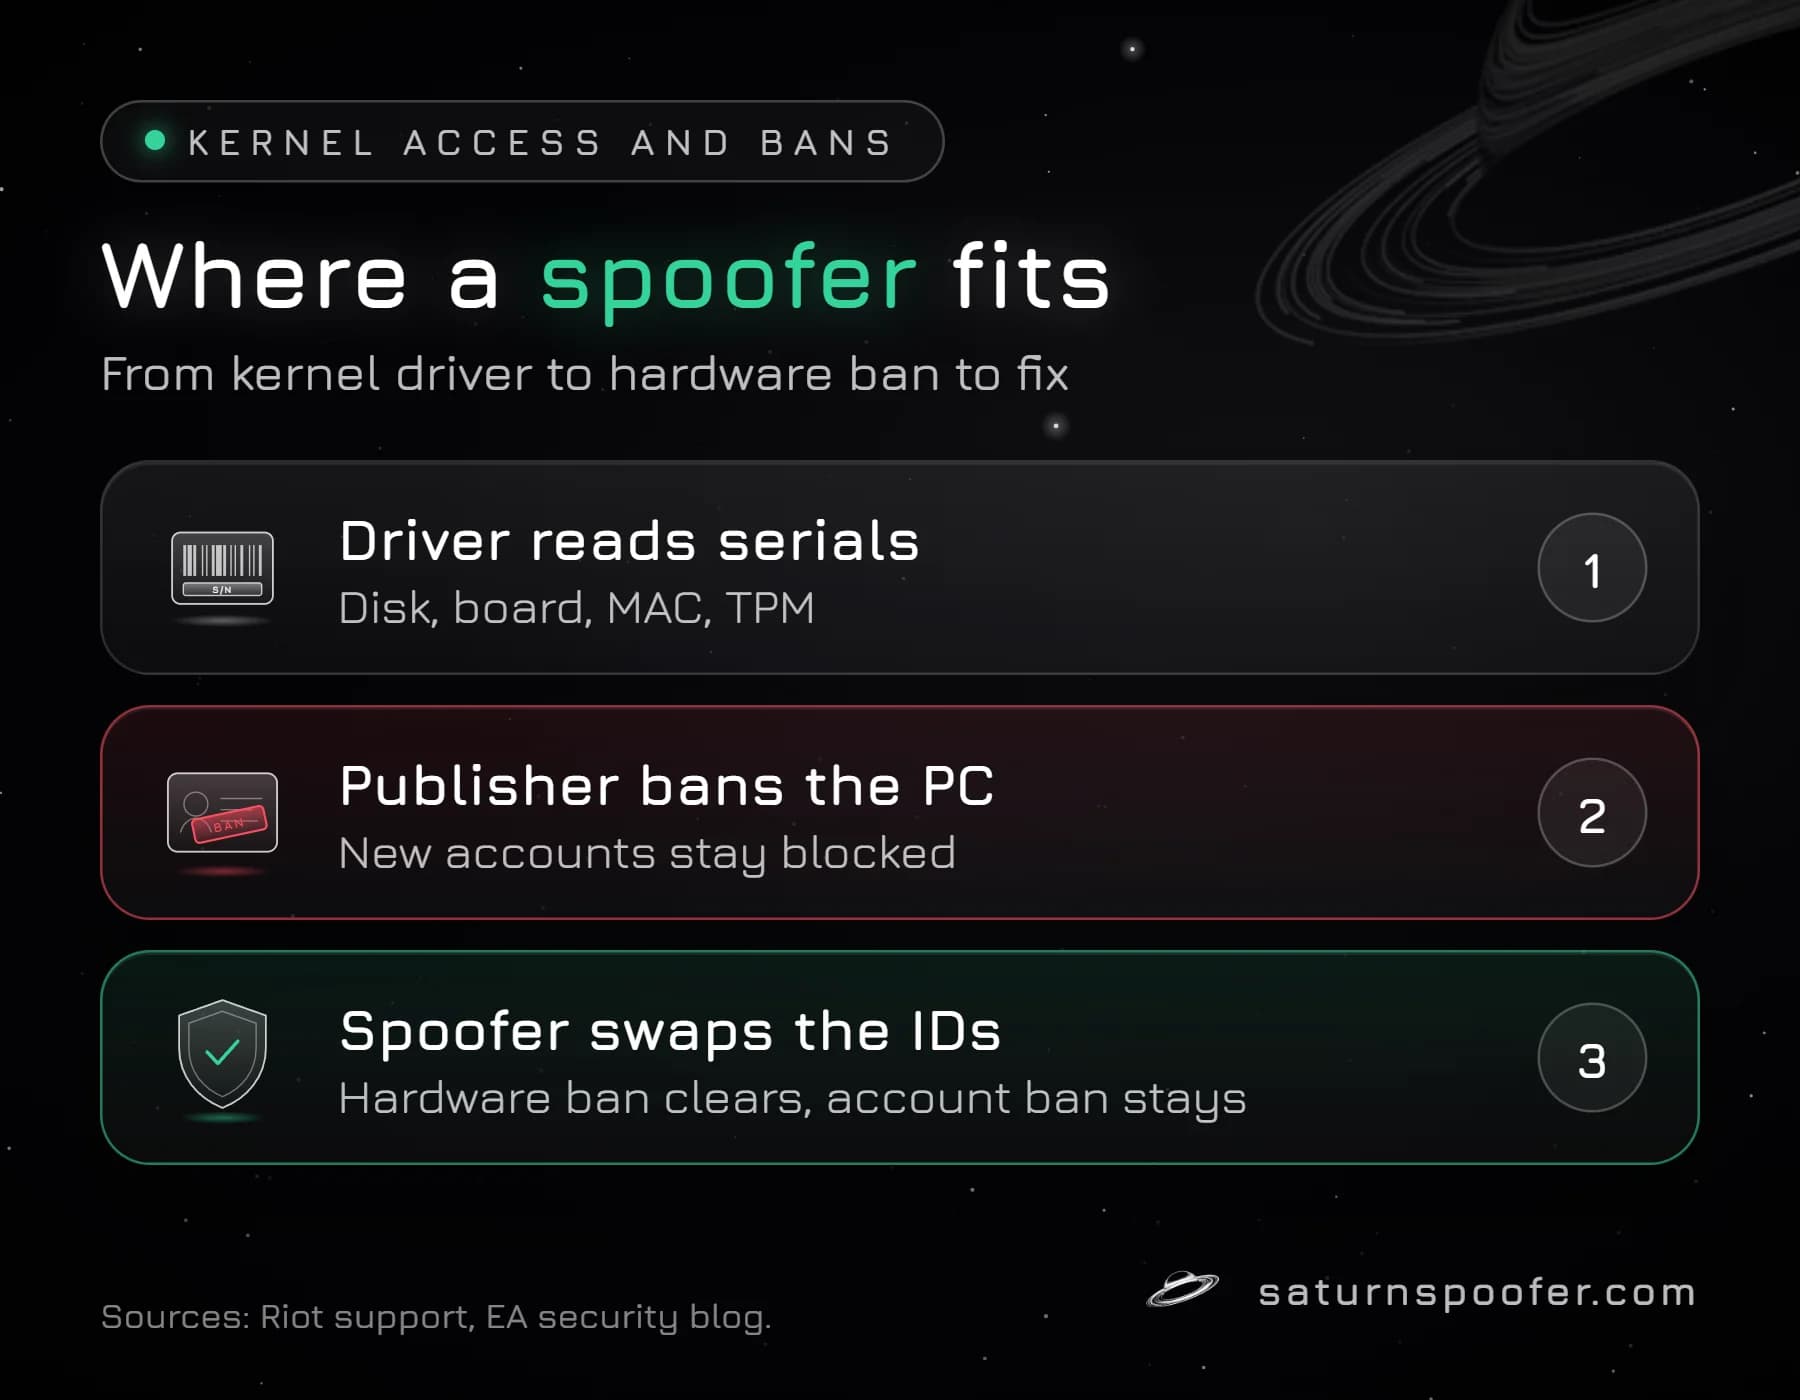
Saturn fits into that one part of the picture. Built for Windows, Saturn is an HWID spoofer, and it does nothing to help anyone cheat: when a game has banned a PC's hardware, Saturn gives the anti-cheat different identifiers to read, so the old hardware ban no longer matches that machine. The list reaches from the TPM, CPU and GPU to disk serials on NVMe, SSD and HDD drives, RAM serials, the motherboard with its SMBIOS fields, the network card's MAC, USB devices, the monitor's EDID and UEFI variables, plus dozens of further identifiers a game could log. Any account ban is untouched. One loader serves every one of the anti-cheats Saturn covers, and the license picks which of them are switched on: ACE, BattlEye, EA Javelin, Easy Anti-Cheat, FiveM and Vanguard. In temporary mode the spoofed values hold only while the program runs, profiles are unlimited, and shutting Saturn down brings the banned originals back. In permanent mode the new values stay after a reboot, on one profile; a fresh profile is a new purchase if that one is ever banned. New users get a free trial lasting 24 hours, signing up with an email address and skipping the card step entirely.
Kernel-Level Anti-Cheat FAQ
Is BattlEye kernel-level?
Yes. BattlEye calls its product a kernel-based protection system, its Windows driver is BEDaisy.sys, and Steam lists it under "Uses Kernel Level Anti-Cheat" on games such as DayZ and Escape from Tarkov.
Is Easy Anti-Cheat kernel-level?
On Windows, yes. Easy Anti-Cheat's FAQ says it needs kernel-level access there, and that it runs only while a protected game is open, never at boot.
Does kernel-level anti-cheat run all the time?
That depends on the system. Riot Vanguard normally loads when Windows starts. Easy Anti-Cheat and EA Javelin Anticheat start with a protected game and stop when it closes.
Can you uninstall kernel-level anti-cheat?
Yes. Easy Anti-Cheat deletes its Windows service after you remove your final EAC-protected game, EA anticheat removes itself once no installed game needs it, and Riot documents how to uninstall Vanguard. BattlEye says many games remove it on uninstall and ships Uninstall_BattlEye.bat in many game folders. Steam warns when a game "Requires manual removal after game uninstall", as Rust and DayZ do. A protected game will not run again until its anti-cheat is reinstalled.
Is Valve Anti-Cheat kernel-level?
No. Counter-Strike 2's Steam listing names VAC (Valve Anti-Cheat) as anti-cheat software without the kernel-level label.
Can kernel-level anti-cheat ban your hardware?
Kernel-level anti-cheat collects the hardware identifiers, and the publisher decides whether a ban covers the account, the PC or both. Riot, for example, reserves HWID bans for serious cases such as flagged cheating or repeated abuse across banned accounts.